


Cyber Security Recruitment
Prioritising your organisation’s digital, cyber and risk strategy is critical.
Clicks’ network of vetted, assessed and experienced cyber professionals are ready for permanent or contract placement in your team, or ongoing project support.
You’re in good hands with a Clicks Vertical Specialist
A Clicks Vertical expert is more than a recruiter — they’re a specialist in your domain. They don’t just know who’s available today; they know who’s off-market, and willing to move jobs for the right opportunity. Your opportunity.
The Cyber & Security roles Clicks recruits:
Principal Consultant
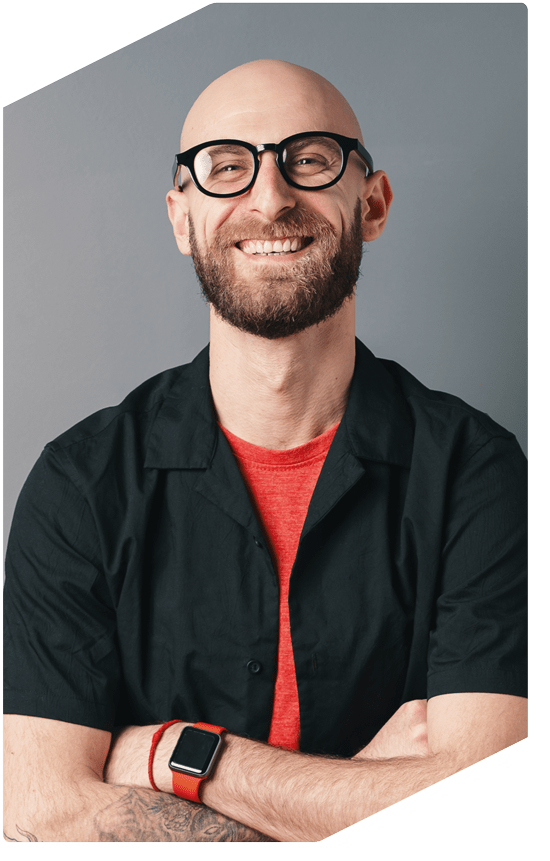
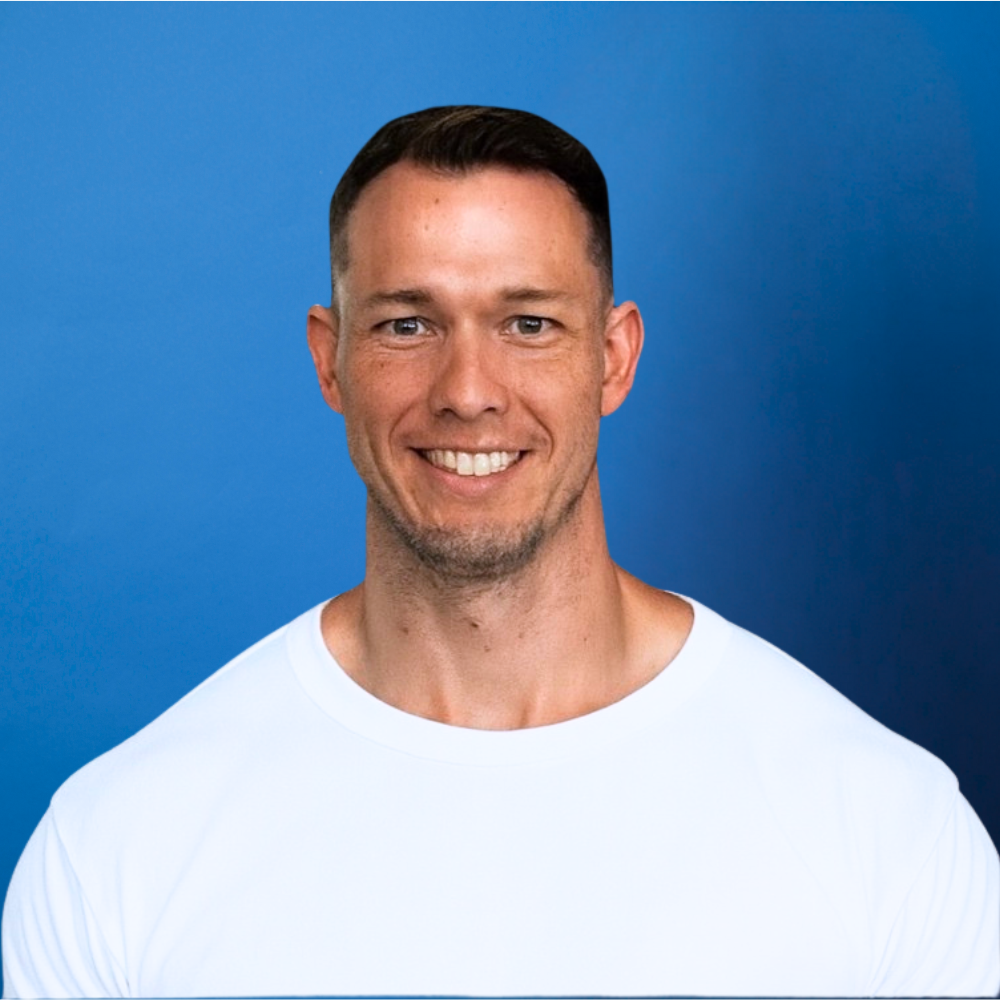
Josh Ainslie
Clicks’ Cyber & Security Lead
Josh specialises in Cyber Security recruitment and has five years of experience partnering with nationally recognised organisations, start-ups and scale-ups. He is committed to securing high-calibre talent while delivering trusted advice, strong outcomes and lasting relationships with clients and candidates.
Our Clients

How We Recruit For You.
Clicks finds people that fit your role, your team, your culture.
With specialist sourcing teams trained across every technology skill vertical and industry for IT, tech and digital recruitment we can people with the experience, expertise to embrace your organisation’s mission, vision and values.
Whether you’re looking to hire a permanent tech expert or contractor, Clicks finds people that become your people.
Book a chat with one of our specialist Cyber Security consultants.
Fill in your details and one of our recruitment specialists will be in touch to chat next steps.
Find the tech people your business needs, backed by award-winning service.
- Specialist Expertise Across Every Technology Vertical — Dedicated teams trained in each tech skill for faster, accurate matching.
- 35+ Years Serving Australia's Largest Employers — 80+ Preferred Supplier Agreements with 92% client retention over the last five years.
- Security-Cleared Talent for Sensitive Environments — Established networks of candidates holding Australian Government security clearances, including Baseline, NV1 and NV2.
- Certified to ISO 9001:2015 — Quality-certified systems and processes built for consistency and continuous improvement.
- Diversity, Built into the Work — We work with trusted partners to widen access to tech careers and support greater representation of women, neurodiverse, LGBTIQA+ and First Nations talent
You’re in Good Hands with Clicks.
A Cyber Security Administrator is responsible for managing an organisation’s cyber security infrastructure. They configure and maintain security controls such as firewalls and intrusion detection systems, and monitor security logs for potential security incidents. Cyber Security Administrators also provide user training and support, and assist with incident response and disaster recovery.
A Cyber Security Analyst protects an organisation’s systems and data by identifying threats, vulnerabilities, and cyber attacks. They monitor network traffic for suspicious activity, respond to security incidents, and conduct risk assessments. They also develop and implement security policies and protocols to safeguard against potential breaches.
A Cyber Security Architect is an expert in designing and implementing secure information technology systems. They are responsible for identifying potential vulnerabilities and designing security controls to protect against cyber attacks. Cyber Security Architects work to ensure the confidentiality, integrity, and availability of information and systems, and stay up to date with emerging threats and technologies.
A Cyber Security Engineer is a professional who is responsible for designing, implementing, and maintaining secure computer systems and networks. Their primary focus is to protect an organization’s computer systems and networks from cyber threats, such as hackers, viruses, and other malicious activities.
A Cyber Security Manager is responsible for managing an organisation’s cyber security program. They develop and implement policies and procedures to mitigate cyber risks, and oversee security operations to ensure the confidentiality, integrity, and availability of an organisation’s data and systems. Cyber Security Managers also provide leadership and guidance to security professionals within the organisation.
Cyber Security Monitoring & Response professionals are responsible for detecting and responding to cyber threats to an organisation’s IT systems. They monitor security logs and conduct real-time analysis of network traffic to identify potential security incidents. Cyber Security Monitoring & Response professionals also develop and implement incident response plans to quickly and effectively respond to security incidents.
A Cyber Security Strategist is a professional responsible for developing and implementing a comprehensive cyber security strategy for an organisation. They work to align cyber security initiatives with business objectives and manage risks to the organisation’s data and systems. Cyber Security Strategists also stay up to date with emerging threats and technologies, and provide guidance to security professionals within the organisation.
A Cyber Threat Engineer is a specialist who anticipates and identifies emerging cyber threats to an organisation’s IT systems. They conduct research and analysis to understand the motivations and tactics of cyber attackers, and develop countermeasures to mitigate risks. Cyber Threat Engineers also provide recommendations for improving an organisation’s security posture.